Overview
A local, read-only registry mirror proxy for dockerd.
A local, read-only registry mirror proxy for dockerd. It sits between dockerd and one or more user-chosen Registry v2 mirrors and adds what dockerd's built-in mirror support lacks:
- Runtime management. Add, remove and disable upstreams without restarting dockerd.
- Failure isolation. A silent or failing mirror costs one timeout, then a circuit breaker takes it out of rotation until a probe succeeds.
- Optional racing. Hedged requests can answer from whichever mirror responds first.
- Resumable layers. A layer that breaks mid-transfer continues from the same byte offset on another mirror, and the daemon still verifies the digest.
- Safe fallback. When the proxy cannot serve a request, dockerd falls back to the official registry, so the proxy can never make a pull impossible.
It supports both dockerd image stores: containerd (hosts.toml) and the classic
graphdriver store (daemon.json, docker.io only).
Installation
Docker deployment
Preview
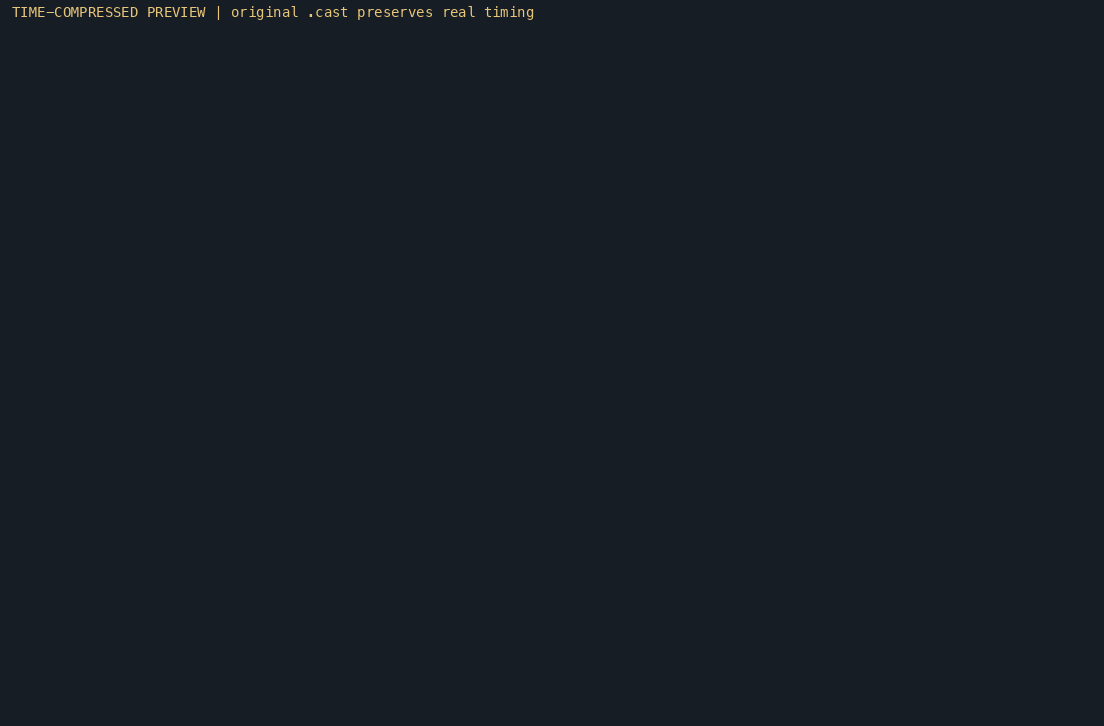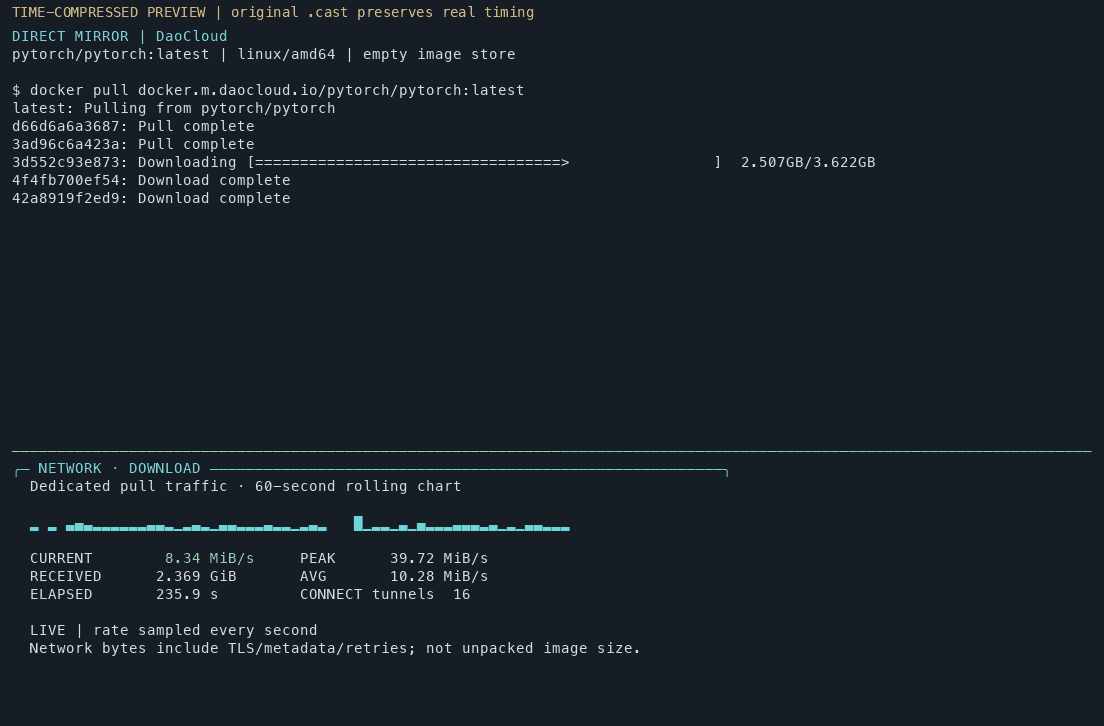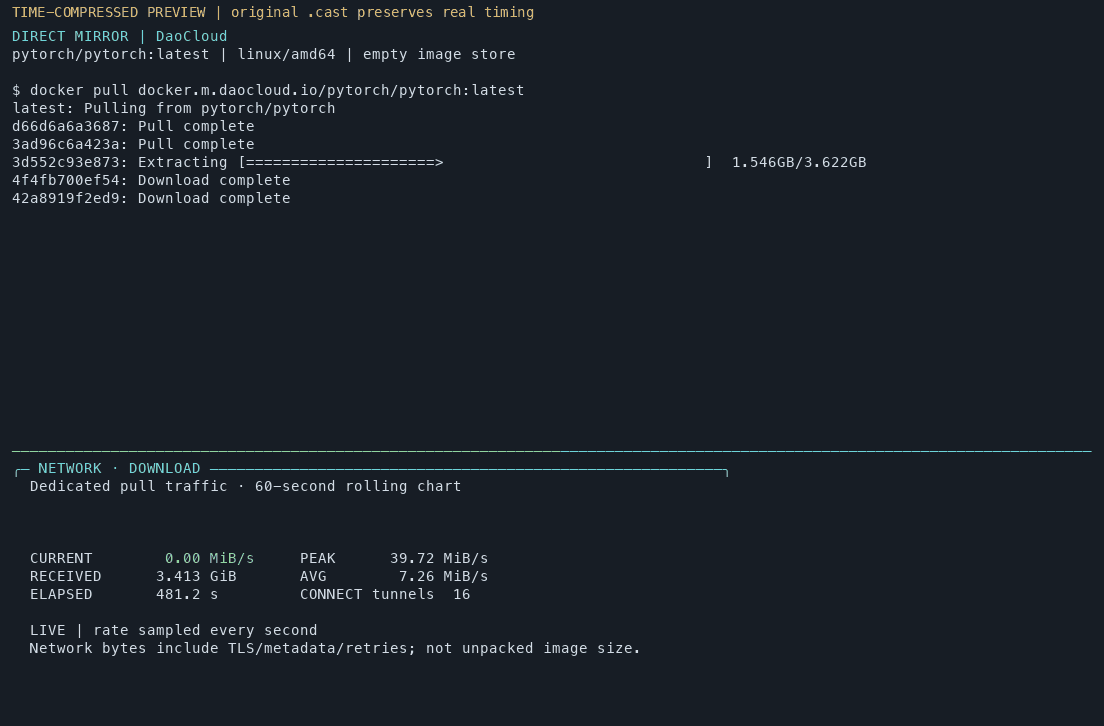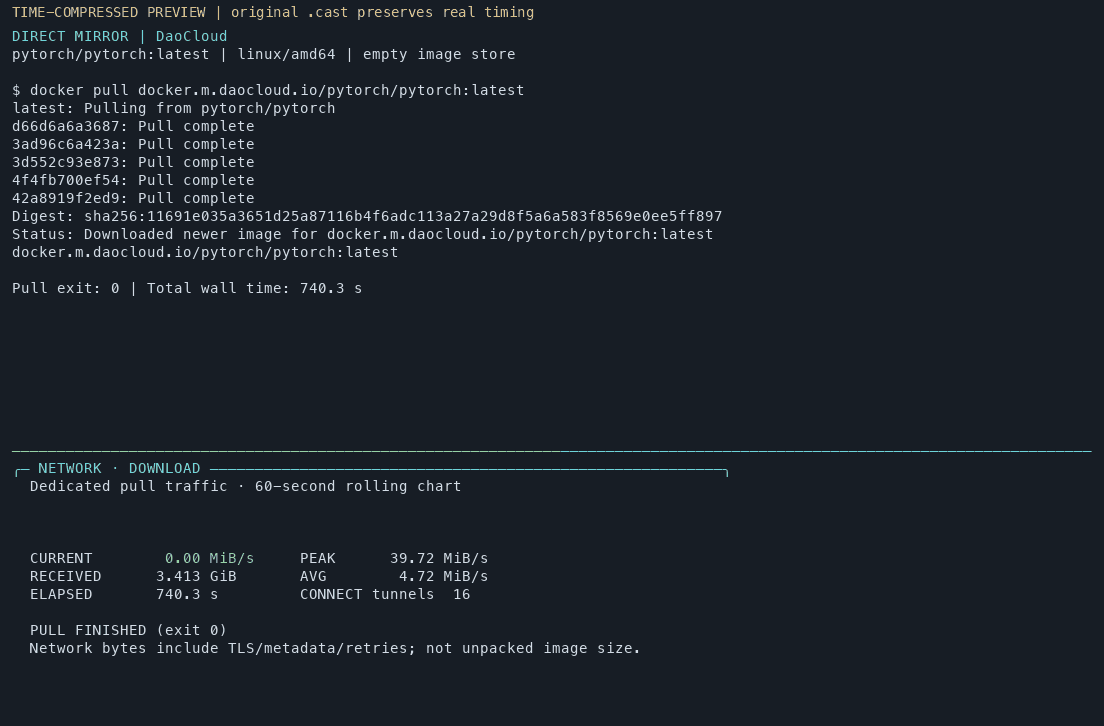
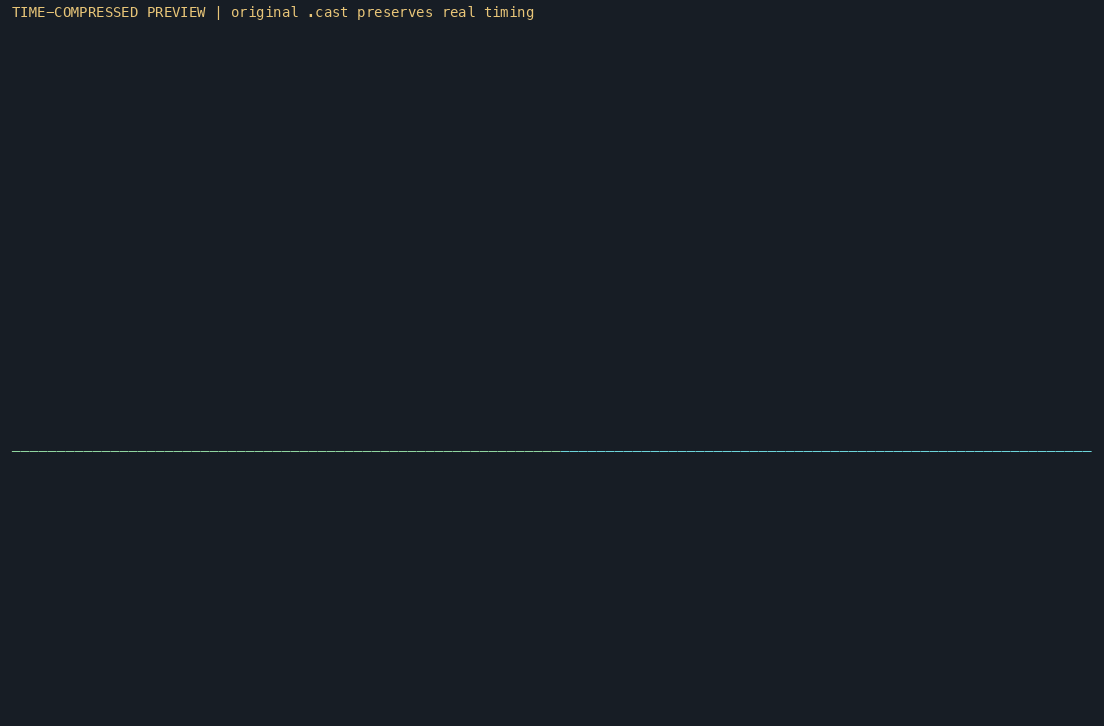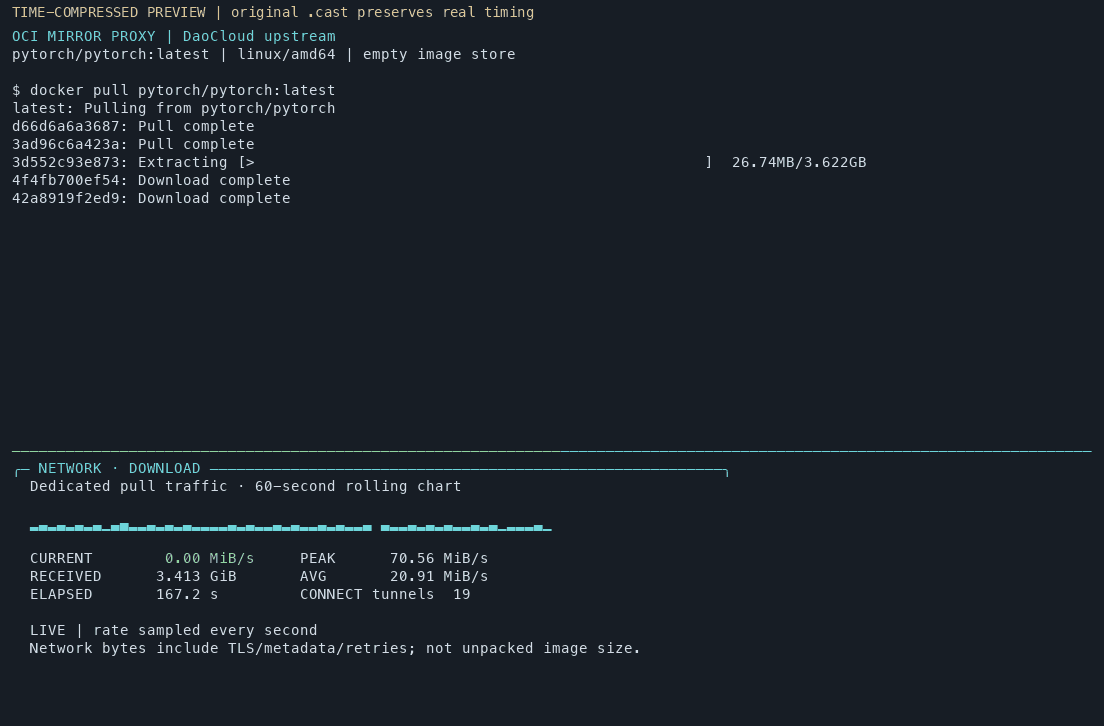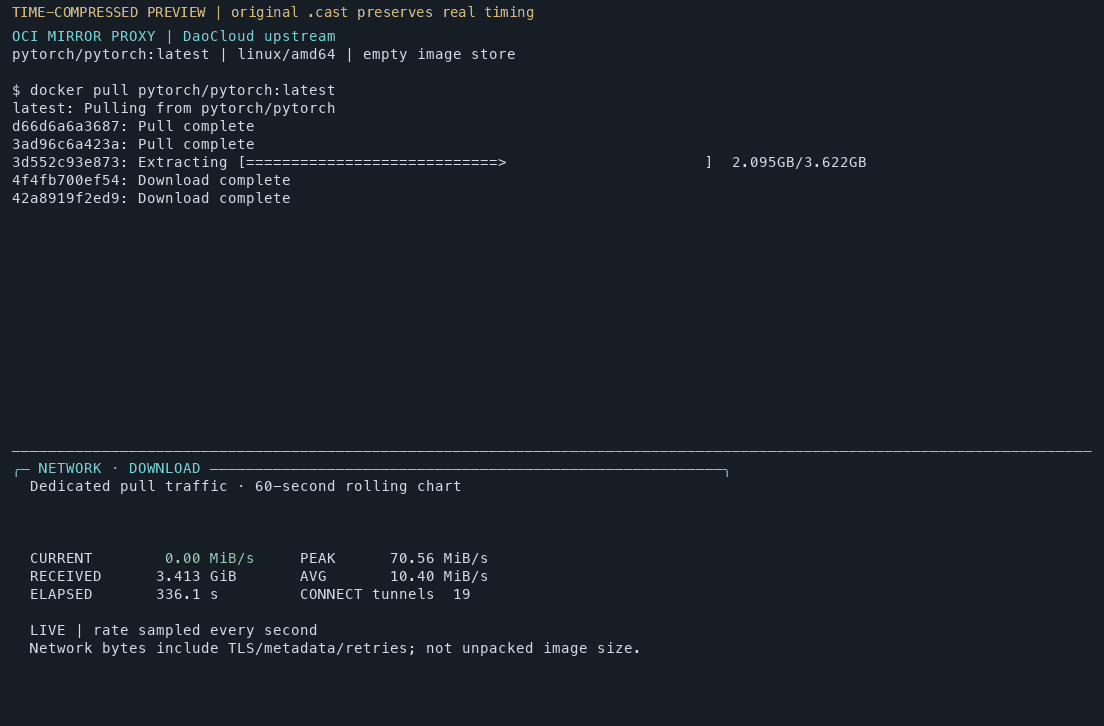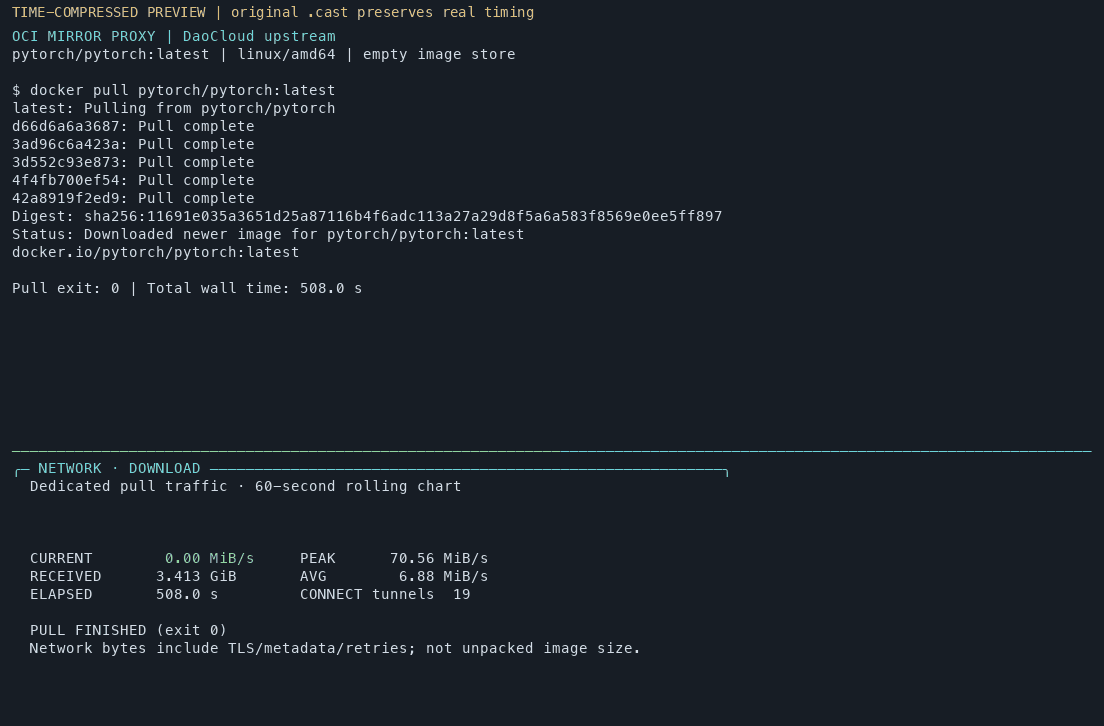
oci-mirror-proxy completed in 508.0 s versus 740.3 s directly from the mirror: 1.46× as fast, or 31.4% less time in this preview.
| Direct mirror · 740.3 s | Through oci-mirror-proxy · 508.0 s |
|---|---|
 |  |
| asciinema recording | asciinema recording |
GIFs are time-compressed previews; the original recordings preserve real timing. See the recording details.
Status
Supported features: the registry API for pulls, failover, circuit breaking, hedged requests, blob resumption, token and basic authentication, the admin socket, configuration reload, and dockerd setup with revert.
Not supported: push, a local blob cache, keychain secret backends, and metrics export.
Requirements
- Go 1.26 or newer, to build.
- A local Docker Engine on Linux or Docker Desktop on macOS/Windows (Linux containers). See automatic Docker integration. Rootless dockerd needs the listen address reachable from its network namespace, which is left to the operator (see rootless dockerd).
Security notes
- The registry API has no authentication, so it listens on
127.0.0.1by default. A non-loopbacklistenexposes unauthenticated pulls to the network. - Credentials never appear in the configuration file: a password is a reference
such as
env:NAMEorfile:/path. Secrets are redacted in logs and in%voutput. - Client
Authorizationheaders are never forwarded upstream. - The admin socket is protected by file permissions: its directory is
0700, and the socket is0600for private instances. Root services using the standard/run/oci-mirror-proxy/admin.sockor/var/run/oci-mirror-proxy/admin.sockendpoint allow all local users to access the management API (0711directory,0666socket), including configuration changes and reloads. Only root can replace the directory or socket; the management API is not exposed over TCP. - Mirror configuration is merged from actual files, without installation state.
Changed files are backed up and atomically replaced;
revertremoves only the selected proxy entries.